Grant De Swardt, an independent AI consultant in the UK, noticed something amiss on August 4: his Claude Max 20x account was burning through tokens even though he was not working. The following day, he shut down everything related to Claude and did not use it for the entire day. Yet token usage kept rising, climbing from 45% to 55%.
De Swardt contacted Anthropic to request an itemized breakdown of the tokens consumed, only to be told that no tool exists allowing users to see what their tokens were spent on. Acknowledging that something was wrong, the company suspended the account, invalidated all active sessions, and issued a partial refund (44.49 British pounds for the remainder of his 200 USD/month plan).
Max 20x usage went from 0% to 100% in half an hour while I was not using Claude
by u/Current_Afternoon_76 in ClaudeAI
Following an investigation, Anthropic informed De Swardt of the cause: a stolen Claude session key had been used to unlawfully mint Claude Code OAuth tokens. His account “appeared to have been used by a third party to process activity for others.” In other words, hackers were quietly draining his tokens without his knowledge.
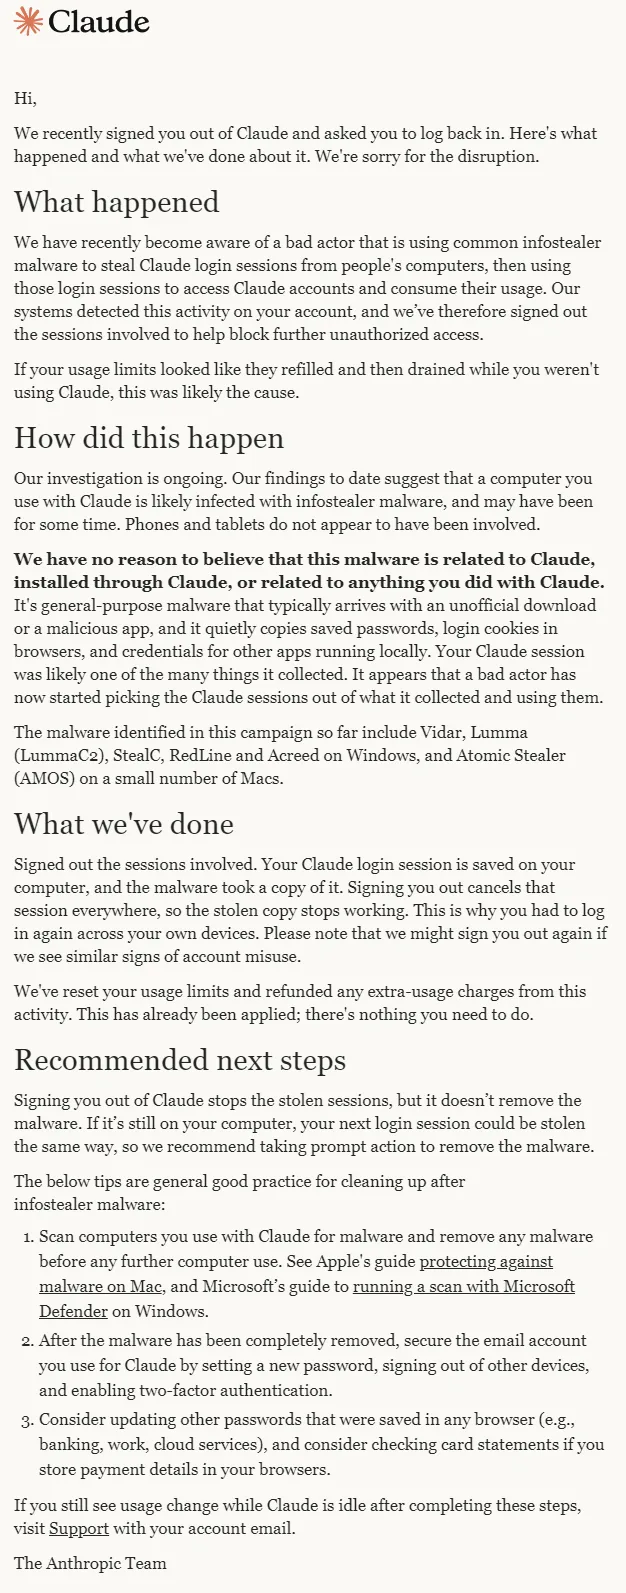
The attack method is not new. Anthropic later sent warning emails to several other users, explaining that “a bad actor is using widespread infostealer malware to harvest Claude login sessions from users’ machines, then using those sessions to access accounts and consume usage limits.” Infostealers are a type of malware that installs itself on a victim’s machine to siphon saved passwords, session data, and login credentials.
Troublingly, De Swardt was not among those who received the warning email. He maintained that he found no evidence of his computer being compromised, and he was still unable to determine how the hackers gained access.
On Reddit, De Swardt’s post drew numerous comments from users with similar experiences. One noted that their account “auto upgraded without consent, credit card charged, and usage went from 0% to 100% in half an hour while not touching it.” Another saw usage jump from 0 to 49% in just 12 minutes, despite running only a few prompts and a single search.
On GitHub, several other users shared comparable stories. One reported their tokens being drained every day for three consecutive days without any usage. Two of them received emails from Anthropic confirming that their tokens were being stolen.
Anthropic handled the incidents by logging out affected users, revoking existing authorizations, issuing refunds, and warning about potential malware infections. However, the company provides no tool enabling users to independently verify what consumed their tokens. When asked by TechCrunch how users could protect themselves, Anthropic declined to comment.
De Swardt eventually had his account restored after about two weeks. But the ordeal prompted him to cancel his Claude subscription and migrate to Cursor, where he can access multiple different models, including lower-cost open-source alternatives. In his view, the other models are “not noticeably different or better” than Claude.
The incident raises questions about the responsibility AI companies bear in protecting their users. When an AI service becomes an essential part of daily life and work, the lack of transparency around token consumption and account security is not merely an inconvenience—it is a serious risk. Users paying 200 USD per month deserve to know what their tokens are being spent on, and to be protected against attacks they cannot detect.